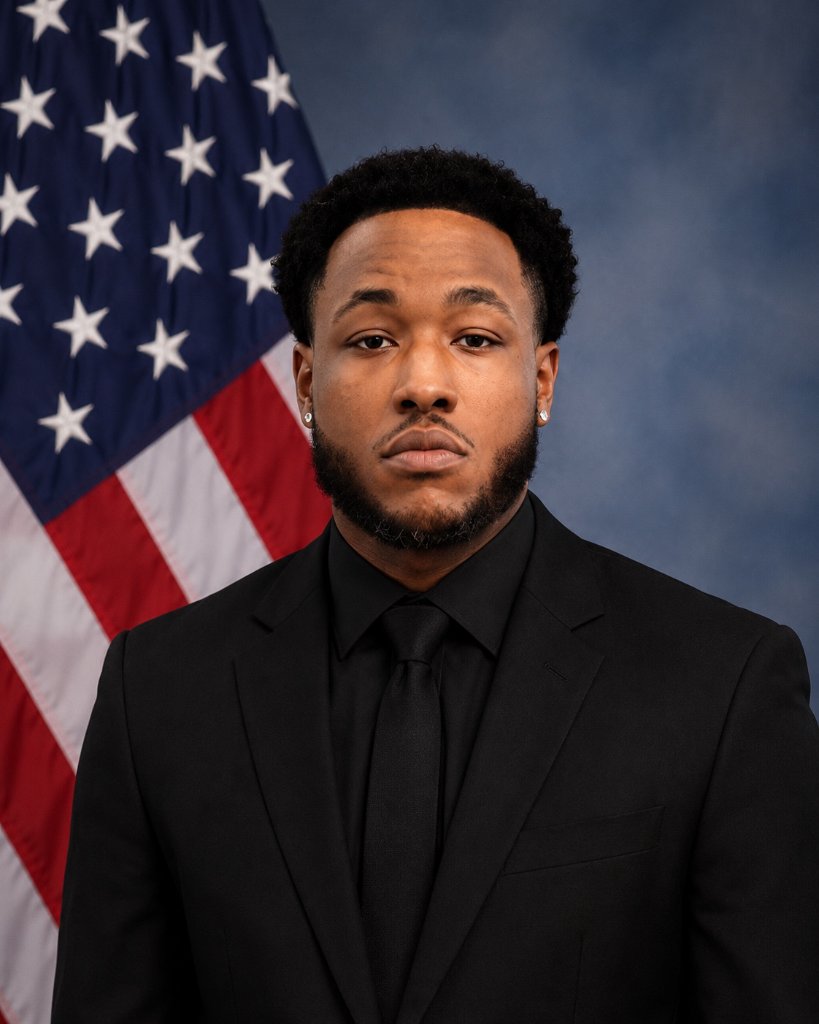
Our founders come from cybersecurity. That background gave Cyber Defense Group its name and informs our attention to requirements, evidence, and clear communication.
Our work centers on system security documentation, control assessment, vulnerability findings and the policies that define how security is carried out.
We start with the system context, applicable requirements, current artifacts and the deliverables your team needs. From there, we define responsibilities and a reviewable scope.
We support the security work and evidence needed for informed decisions. System owners and authorizing officials retain their approval and risk-acceptance responsibilities.
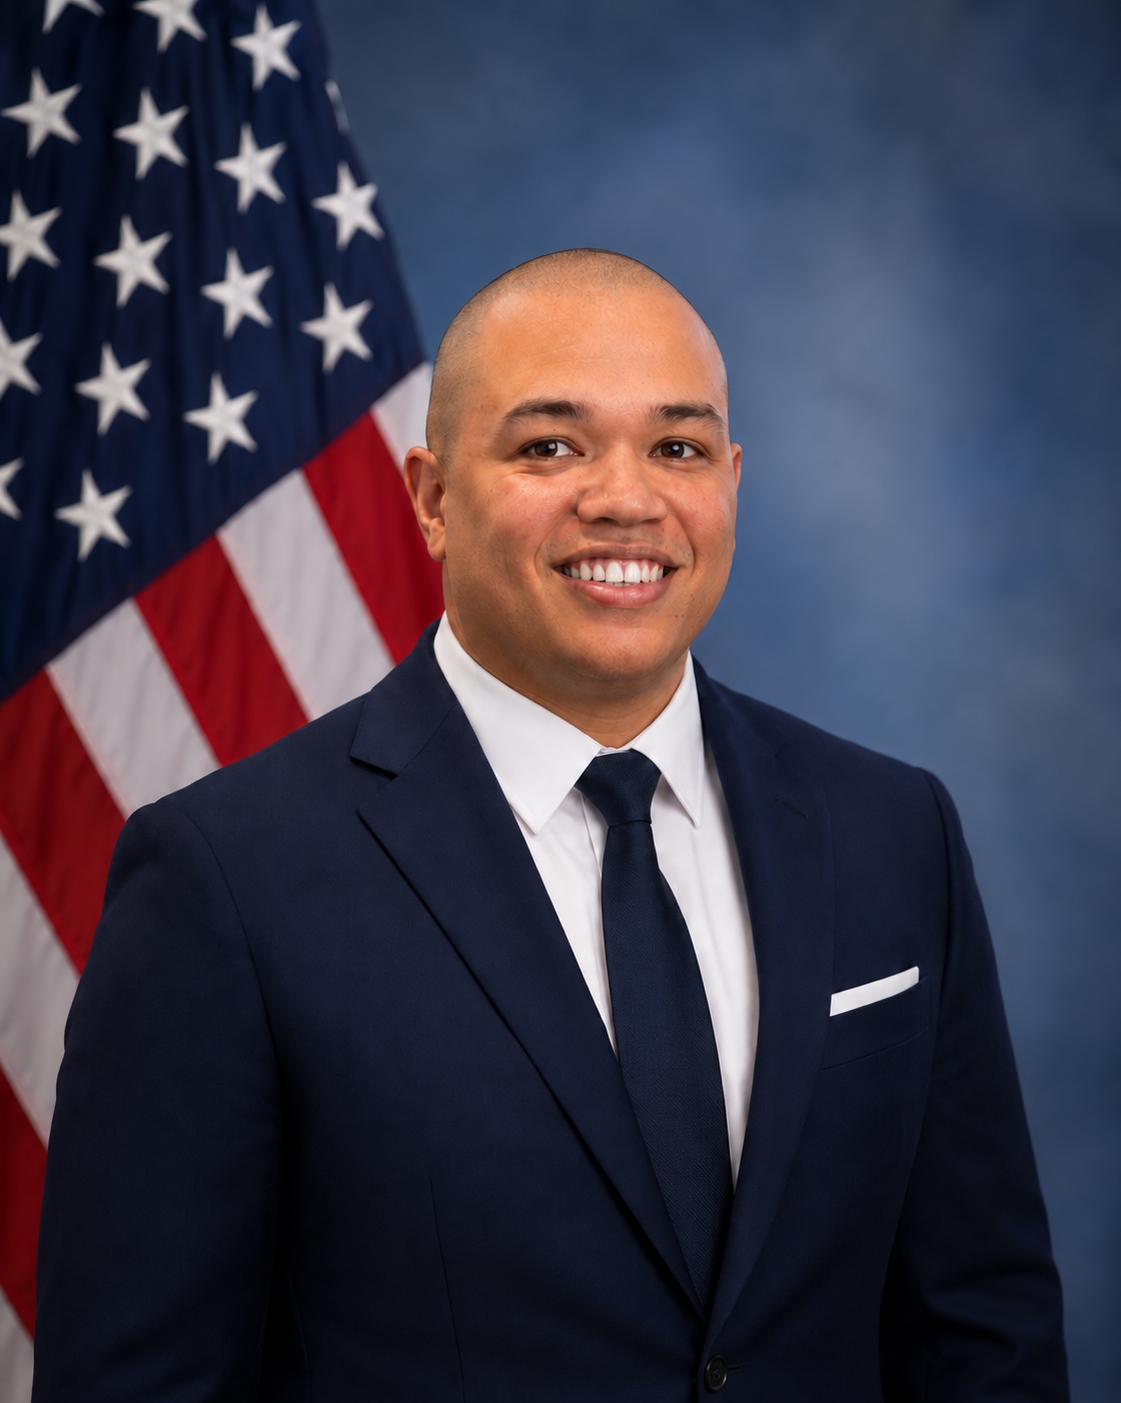 Co-Founder